YEO CFR SDK
Continuous Facial Recognition SDK
Give your platform the ability to confirm the right person is present, not just at login, but throughout the entire session.


Trusted by Teams in:
KYC Identity Verification
Child Safety Online
Banking & Finance
Cyber Security
Insurance
Social Communities
Government
Public Authorities
Legal
THE PROBLEM WITH STATIC AUTHENTICATION
You can't trust who's behind the screen.
Static authentication (a password, a PIN, a one-time login check) confirms that someone presented the right credentials. It does not confirm that the right person is present. In a world of credential theft, deepfake technology, and AI-generated impersonation, that gap is no longer theoretical.
Identity Fraud & Account Takeovers
Stolen credentials, SIM swaps, and account takeover are the fastest-growing categories of digital fraud. Continuous verification closes the session-level window.
Deepfake & Synthetic Media Threats
Broken Age Verification
Regulatory & Compliance Pressure


Static authentication (a password, a PIN, a one-time login check) confirms that someone presented the right credentials. It does not confirm that the right person is present. In a world of credential theft, deepfake technology, and AI-generated impersonation, that gap is no longer theoretical.
Identity Fraud & Account Takeovers
Stolen credentials, SIM swaps, and account takeover are the fastest-growing categories of digital fraud. Continuous verification closes the session-level window.
Deepfake & Synthetic Media Threats
Broken Age Verification
Regulatory & Compliance Pressure
Static authentication (a password, a PIN, a one-time login check) confirms that someone presented the right credentials. It does not confirm that the right person is present. In a world of credential theft, deepfake technology, and AI-generated impersonation, that gap is no longer theoretical.
Identity Fraud & Account Takeovers
Stolen credentials, SIM swaps, and account takeover are the fastest-growing categories of digital fraud. Continuous verification closes the session-level window.
Deepfake & Synthetic Media Threats
Broken Age Verification
Regulatory & Compliance Pressure
OUR SOLUTION
Continuous protection, built into every session
Real-Time Continuous Authentication
Verify users throughout their session, not just at login. Unauthorised access attempts are detected instantly.
Biometrics Stored Locally
Privacy-first compliance, biometric data is never centralised. Meet age-gating regulations without collecting ID documents or storing sensitive biometric data.

Stay Ahead of Fraud
Multi-layer liveness detection defeats AI-generated faces, printed photos, and masks. Presentation attack detection certified and continuous.
Compliance-Ready by Default
Built for Online Safety Bill, GDPR, and age-gating regulations. Audit-ready, documentation-rich, designed for regulated industries.
Real-Time Continuous Authentication
Verify users throughout their session, not just at login. Unauthorised access attempts are detected instantly.
Biometrics Stored Locally
Privacy-first compliance, biometric data is never centralised. Meet age-gating regulations without collecting ID documents or storing sensitive biometric data.
Stay Ahead of Fraud
Multi-layer liveness detection defeats AI-generated faces, printed photos, and masks. Presentation attack detection certified and continuous.
Compliance-Ready by Default
Built for Online Safety Bill, GDPR, and age-gating regulations. Audit-ready, documentation-rich, designed for regulated industries.
The Technology
What is continuous facial recognition?
Continuous identity verification means confirming that the right person is present throughout a digital session, not only at the point of entry. YEO's technology runs 3 layers passively in the background, verifying presence at regular intervals and at key points, without interrupting the user experience for legitimate users.

Layer 1
Advanced Facial Mapping
Establishes a precise geometric model of the authorised user's facial structure at enrolment. Captures spatial relationships between facial landmarks (the geometry of the face), not a photographic image.
Developers configure matching threshold to set desired confidence level

PRIVACY FIRST
The enrolled facial model remains on-device.
REDUCE RISKS FROM
Server breach/data exfiltration
Interception in transit
Centralised template compromise
The Technology
What is continuous facial recognition?
Continuous identity verification means confirming that the right person is present throughout a digital session, not only at the point of entry. YEO's technology runs 3 layers passively in the background, verifying presence at regular intervals and at key points, without interrupting the user experience for legitimate users.
Layer 1
Advanced Facial Mapping
Establishes a precise geometric model of the authorised user's facial structure at enrolment. Captures spatial relationships between facial landmarks (the geometry of the face), not a photographic image.
Developers configure matching threshold to set desired confidence level
PRIVACY FIRST
The enrolled facial model remains on-device.
REDUCE RISKS FROM
Server breach/data exfiltration
Interception in transit
Centralised template compromise
The Technology
What is continuous facial recognition?
Continuous identity verification means confirming that the right person is present throughout a digital session, not only at the point of entry. YEO's technology runs 3 layers passively in the background, verifying presence at regular intervals and at key points, without interrupting the user experience for legitimate users.
Layer 1
Advanced Facial Mapping
Establishes a precise geometric model of the authorised user's facial structure at enrolment. Captures spatial relationships between facial landmarks (the geometry of the face), not a photographic image.
Developers configure matching threshold to set desired confidence level
PRIVACY FIRST
The enrolled facial model remains on-device.
REDUCE RISKS FROM
Server breach/data exfiltration
Interception in transit
Centralised template compromise
How it differs from one-time facial recognition
Dimension
One-Time
Facial Recognition
YEO'S Continuous
Facial Recognition
When it checks
Once, at login or onboarding
Continuously, throughout the entire session
What it actually proves
The right person opened the session
The right person is still present, at every point
Session handoff / theft risk
Once verified, a device or authenticated session can be handed off, stolen, or left unlocked with no way to detect the swap
Detects if the verified user is replaced or absent mid-session
Deepfake / spoof resistance
A single check is a single target — pass it once (photo, video replay, deepfake) and you're in
Layered, ongoing liveness detection makes sustained spoofing far harder to pull off
Liveness detection
Typically one liveness check at the moment of verification
Runs continuously as part of the same passive session check
Data & privacy model
Many one-time flows capture and store a selfie or ID image server-side
Facial model stays on-device; nothing transmitted or centrally stored
Compliance evidence
Proves identity was checked once — leaves a gap for everything after
Provides an ongoing audit trail of presence, closer to what regulators (FCA/SMCR, Online Safety Act, age-gating rules) actually expect
User experience
Explicit action required (take a selfie, scan your face) at set checkpoints — interrupts the flow
Passive and background — no repeated prompts or interruptions
Typical use case
Onboarding, KYC, single login
Ongoing session security and one off — Onboarding, KYC, single login, messaging platforms, insider risk, age-gating for the duration of use
Dimension
One-Time
Facial Recognition
YEO'S Continuous
Facial Recognition
When it checks
Once, at login or onboarding
Continuously, throughout the entire session
What it actually proves
The right person opened the session
The right person is still present, at every point
Session handoff / theft risk
Once verified, a device or authenticated session can be handed off, stolen, or left unlocked with no way to detect the swap
Detects if the verified user is replaced or absent mid-session
Deepfake / spoof resistance
A single check is a single target — pass it once (photo, video replay, deepfake) and you're in
Layered, ongoing liveness detection makes sustained spoofing far harder to pull off
Liveness detection
Typically one liveness check at the moment of verification
Runs continuously as part of the same passive session check
Data & privacy model
Many one-time flows capture and store a selfie or ID image server-side
Facial model stays on-device; nothing transmitted or centrally stored
Compliance evidence
Proves identity was checked once — leaves a gap for everything after
Provides an ongoing audit trail of presence, closer to what regulators (FCA/SMCR, Online Safety Act, age-gating rules) actually expect
User experience
Explicit action required (take a selfie, scan your face) at set checkpoints — interrupts the flow
Passive and background — no repeated prompts or interruptions
Typical use case
Onboarding, KYC, single login
Ongoing session security and one off — Onboarding, KYC, single login, messaging platforms, insider risk, age-gating for the duration of use
intergration
Ready to integrate on any platform, at any stage
The YEO CFR SDK integrates at the application layer — no infrastructure changes, no rip-and-replace. Drop it into iOS, Android, or web and add continuous identity verification to your platform without touching what already works.


Layer With Existing ID Verification
The SDK adds continuous session verification without displacing your existing KYC, authentication, or onboarding infrastructure. It works alongside your current stack, not instead of it.
Up and running in as little as 3 days
Application-layer integration means minimal engineering overhead. Full technical documentation, SDK packages and dedicated support are available from day one. Most integrations go live within three days of starting.
White-label options to match your brand
The SDK runs inside your product, under your brand. No YEO interface, no third-party screens — fully customisable to your design system so verification feels native to your platform.
Choose where and when it's active.
Run continuous verification throughout every session, or activate it only at critical moments — high-value transactions, sensitive data access, or account changes. You define the policy.

Frictionless customer experience
Most security adds steps. YEO removes the need for them. The CFR SDK runs passively on-device throughout every session — confirming the right person is present without prompting, interrupting or asking anything of your users. Legitimate customers experience nothing different. The only layer that changes is the one your platform never had: continuous verification that works invisibly, from login to sign-out.
Frictionless customer experience
Most security adds steps. YEO removes the need for them. The CFR SDK runs passively on-device throughout every session — confirming the right person is present without prompting, interrupting or asking anything of your users. Legitimate customers experience nothing different. The only layer that changes is the one your platform never had: continuous verification that works invisibly, from login to sign-out.
Frictionless customer experience
Most security adds steps. YEO removes the need for them. The CFR SDK runs passively on-device throughout every session — confirming the right person is present without prompting, interrupting or asking anything of your users. Legitimate customers experience nothing different. The only layer that changes is the one your platform never had: continuous verification that works invisibly, from login to sign-out.
A continuous verification solution for all industries
YEO's technology is deployed across industries where identity, accountability, and data integrity are not optional extras, they are foundational requirements.

KYC Identity Verification
Learn moreKnow Your Customer compliance has always been about the moment of onboarding. The threat has moved to what happens in every session after that.

Child Safety Online
Learn moreThe Online Safety Act requires platforms to know who is accessing their service. It does not yet require them to verify who remains present throughout the session.

Banking & Finance
Learn moreAccount takeover, APP fraud, and session hijacking all operate inside authenticated sessions. The controls the industry has invested in were built for a different threat.

Cyber Security
Learn moreModern cyber attacks don't force the door. They walk through it — impersonating trusted identities, operating inside authenticated sessions, and exploiting the trust that follows a legitimate login.

Insurance
Learn moreClaims fraud, impersonation, and unverified session access are costing the insurance sector billions. The controls protecting the point of entry are not protecting what happens inside it.

Social Communities
Learn MoreAccount sharing, impersonation, and unverified presence are the defining integrity challenges for social platforms. Verification at registration only solves part of the problem.

Government
Learn MoreWhen decisions carry public accountability and communications may be subject to disclosure, the standard for evidencing who said what — and who was present when they said it — is not optional.
Public Authorities
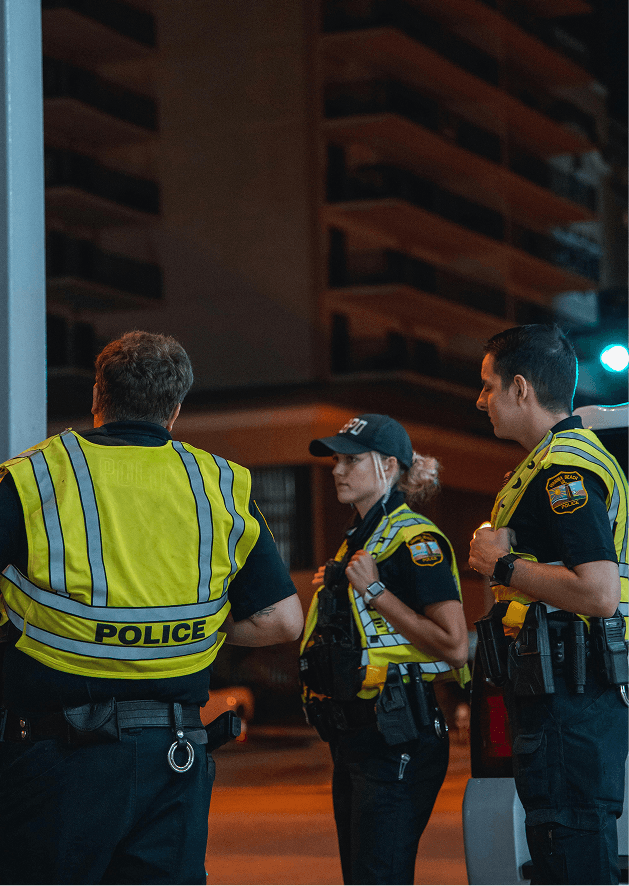
Learn MorePublic authorities handling sensitive information, enforcement decisions, and community communications need communications infrastructure that can stand behind every action taken in their name.

Scale with ease
Because verification runs entirely on-device, there is no server infrastructure to provision, maintain or upgrade as your user base grows. Each device handles its own processing load — which means scaling is a matter of adding users, not adding servers. No infrastructure overhead, no bottlenecks, no backend costs that compound as you grow.
Scale with ease
Because verification runs entirely on-device, there is no server infrastructure to provision, maintain or upgrade as your user base grows. Each device handles its own processing load — which means scaling is a matter of adding users, not adding servers. No infrastructure overhead, no bottlenecks, no backend costs that compound as you grow.
Scale with ease
Because verification runs entirely on-device, there is no server infrastructure to provision, maintain or upgrade as your user base grows. Each device handles its own processing load — which means scaling is a matter of adding users, not adding servers. No infrastructure overhead, no bottlenecks, no backend costs that compound as you grow.



What users are saying


Explore more:
Pricing model
YEO CFR SDK is offered under a yearly subscription model, with pricing based on the number of mobile users using the technology. This approach allows customers to align their investment with the scale of their deployment, providing a predictable and transparent cost as their user base grows.

Standard SaaS Subscription
Basic
Annual subscription
Priced according to the number of mobile users
Predictable annual expenditure
Scales as the customer user base grows
Suitable for initial deployments, pilots, and smaller-scale production environments.
Enterprise Software Licence
Enterprise
Negotiated for larger deployments
Designed for significant or strategic enterprise adoption
Provides greater flexibility for customer growth
Can cover multiple applications, business units or deployment environments
Enables customers to expand their security capabilities without being constrained by a traditional per-user model
Particularly suited to organisations looking to deploy YEO CFR across multiple applications, business units, geographies or large user populations.
FAQ's
Have questions? Explore our FAQ's to find quick answers or reach out to our support team for personalised assistance. We're here to help you get the most out of YEO for Business.
What is the YEO CFR SDK?
The YEO CFR SDK (Continuous Facial Recognition Software Development Kit) is a biometric identity verification layer that integrates directly into existing applications. It verifies that the account holder is present and in control of their session — continuously, passively, and entirely on-device — rather than only at login.
How does the CFR SDK work?
The SDK runs three verification layers in combination. Advanced Facial Mapping builds a precise biometric model of the enrolled user. Anti-Spoofing Liveness Detection distinguishes a live person from a photograph, video replay, or AI-generated deepfake. Depth Verification confirms physical presence, distinguishing a live face from a screen or mask. All three layers process on the user's device. If the verified account holder is no longer present, the platform receives a real-time policy trigger, which the integrating application can act on according to its own rules.
Is biometric data stored or transmitted?
No. All biometric processing happens on the user's device. No image, template, or biometric data is transmitted to YEO's servers or any external system. There is no central biometric database. This is an architectural fact, not a policy promise — there is no transmission pathway to remove data from.
Is the CFR SDK patented?
Yes. YEO holds patents in the US, the UK, the EU, and China, covering the continuous facial recognition technology stack. The patents are valid until 2038.
How does the SDK integrate?
Integration is at SDK level, meaning it does not require changes to a platform's existing authentication infrastructure. It runs alongside existing login systems rather than replacing them. Most integrations go live within days of the technical handshake being completed.
FAQ's
Have questions? Explore our FAQ's to find quick answers or reach out to our support team for personalised assistance. We're here to help you get the most out of YEO for Business.
What is the YEO CFR SDK?
The YEO CFR SDK (Continuous Facial Recognition Software Development Kit) is a biometric identity verification layer that integrates directly into existing applications. It verifies that the account holder is present and in control of their session — continuously, passively, and entirely on-device — rather than only at login.
How does the CFR SDK work?
The SDK runs three verification layers in combination. Advanced Facial Mapping builds a precise biometric model of the enrolled user. Anti-Spoofing Liveness Detection distinguishes a live person from a photograph, video replay, or AI-generated deepfake. Depth Verification confirms physical presence, distinguishing a live face from a screen or mask. All three layers process on the user's device. If the verified account holder is no longer present, the platform receives a real-time policy trigger, which the integrating application can act on according to its own rules.
Is biometric data stored or transmitted?
No. All biometric processing happens on the user's device. No image, template, or biometric data is transmitted to YEO's servers or any external system. There is no central biometric database. This is an architectural fact, not a policy promise — there is no transmission pathway to remove data from.
Is the CFR SDK patented?
Yes. YEO holds patents in the US, the UK, the EU, and China, covering the continuous facial recognition technology stack. The patents are valid until 2038.
How does the SDK integrate?
Integration is at SDK level, meaning it does not require changes to a platform's existing authentication infrastructure. It runs alongside existing login systems rather than replacing them. Most integrations go live within days of the technical handshake being completed.
FAQ's
Have questions? Explore our FAQ's to find quick answers or reach out to our support team for personalised assistance. We're here to help you get the most out of YEO for Business.
What is the YEO CFR SDK?
The YEO CFR SDK (Continuous Facial Recognition Software Development Kit) is a biometric identity verification layer that integrates directly into existing applications. It verifies that the account holder is present and in control of their session — continuously, passively, and entirely on-device — rather than only at login.
How does the CFR SDK work?
The SDK runs three verification layers in combination. Advanced Facial Mapping builds a precise biometric model of the enrolled user. Anti-Spoofing Liveness Detection distinguishes a live person from a photograph, video replay, or AI-generated deepfake. Depth Verification confirms physical presence, distinguishing a live face from a screen or mask. All three layers process on the user's device. If the verified account holder is no longer present, the platform receives a real-time policy trigger, which the integrating application can act on according to its own rules.
Is biometric data stored or transmitted?
No. All biometric processing happens on the user's device. No image, template, or biometric data is transmitted to YEO's servers or any external system. There is no central biometric database. This is an architectural fact, not a policy promise — there is no transmission pathway to remove data from.
Is the CFR SDK patented?
Yes. YEO holds patents in the US, the UK, the EU, and China, covering the continuous facial recognition technology stack. The patents are valid until 2038.
How does the SDK integrate?
Integration is at SDK level, meaning it does not require changes to a platform's existing authentication infrastructure. It runs alongside existing login systems rather than replacing them. Most integrations go live within days of the technical handshake being completed.
Latest News & Insights


Latest News & Insights
Latest News & Insights



See continuous identity verification in action
See how YEO's continuous facial recognition technology works, and what it can do for your platform or team.


See continuous identity verification in action
See how YEO's continuous facial recognition technology works, and what it can do for your platform or team.
See continuous identity verification in action
See how YEO's continuous facial recognition technology works, and what it can do for your platform or team.
© 2026 YEO messaging Ltd is registered in England and Wales 10785061.
🇺🇸 US Patent No: 10,607,035 (Granted March 31, 2020)
🇬🇧 GB patent No: 1713943.7 (Granted February 2022)
🇨🇳 Chinese patent 201880071020.4 (Granted April 2nd 2024)
🇪🇺 EU patent No: PCT/EP2018/073464 (Granted July 2026)
© 2026 YEO messaging Ltd is registered in England and Wales 10785061.
🇺🇸 US Patent No: 10,607,035 (Granted March 31, 2020)
🇬🇧 GB patent No: 1713943.7 (Granted February 2022)
🇨🇳 Chinese patent 201880071020.4 (Granted April 2nd 2024)
🇪🇺 EU patent No: PCT/EP2018/073464 (Granted July 2026)
© 2026 YEO messaging Ltd is registered in England and Wales 10785061.
🇺🇸 US Patent No: 10,607,035 (Granted March 31, 2020)
🇬🇧 GB patent No: 1713943.7 (Granted February 2022)
🇨🇳 Chinese patent 201880071020.4 (Granted April 2nd 2024)
🇪🇺 EU patent No: PCT/EP2018/073464 (Granted July 2026)