Authentication at login is no longer enough. The fraud is already inside.
Account takeover, APP fraud, and session hijacking all operate inside authenticated sessions. The controls the industry has invested in were built for a different threat.


The problem
UK banks lost over £500 million to authorised push payment fraud in 2024. US account takeover losses reached $15.6 billion. In both cases, the dominant attack vector is not a failed authentication event — it is a successful one, followed by a fraudulent session. Stolen session cookies allow attackers to resume authenticated sessions without triggering a new login. Coaching fraud operates entirely inside legitimate sessions where the account holder has authenticated correctly. AI-enabled impersonation is defeating MFA workflows at the entry point. CrowdStrike found that MFA failed to prevent the attack in 84% of account takeover incidents — not because MFA is broken, but because the attack enters through or after authentication. The industry has built strong doors. The room behind them is still unverified.
£500m+
UK authorised push payment fraud losses, 2024. All operating inside authenticated sessions, not through broken logins.
$15.6bn
US account takeover losses, 2024. The dominant attack vector: a successful authentication event, followed by a fraudulent session.
84%
ATO incidents where MFA failed to prevent the breach (CrowdStrike). Attacks enter through or after authentication, not before it.
Discover how YEO can protect banking & finance
Stop Fraud Inside the Session
Continuous presence-checking at the point of transaction, not just at login.
No displacement of existing authentication infrastructure — integrates at SDK level.
Evidence Regulatory Accountability
A verified audit trail showing not just what was communicated, but who communicated it.
Aligned to SMCR, MiFID II, and FCA Consumer Duty.
Deploy Without Disruption
SDK-level integration, live within days.
No rip-and-replace of what's already working in your authentication stack.
Relevant Solutions
Solutions for banking & finance
Together, YEO's products address both sides of the financial services identity problem.
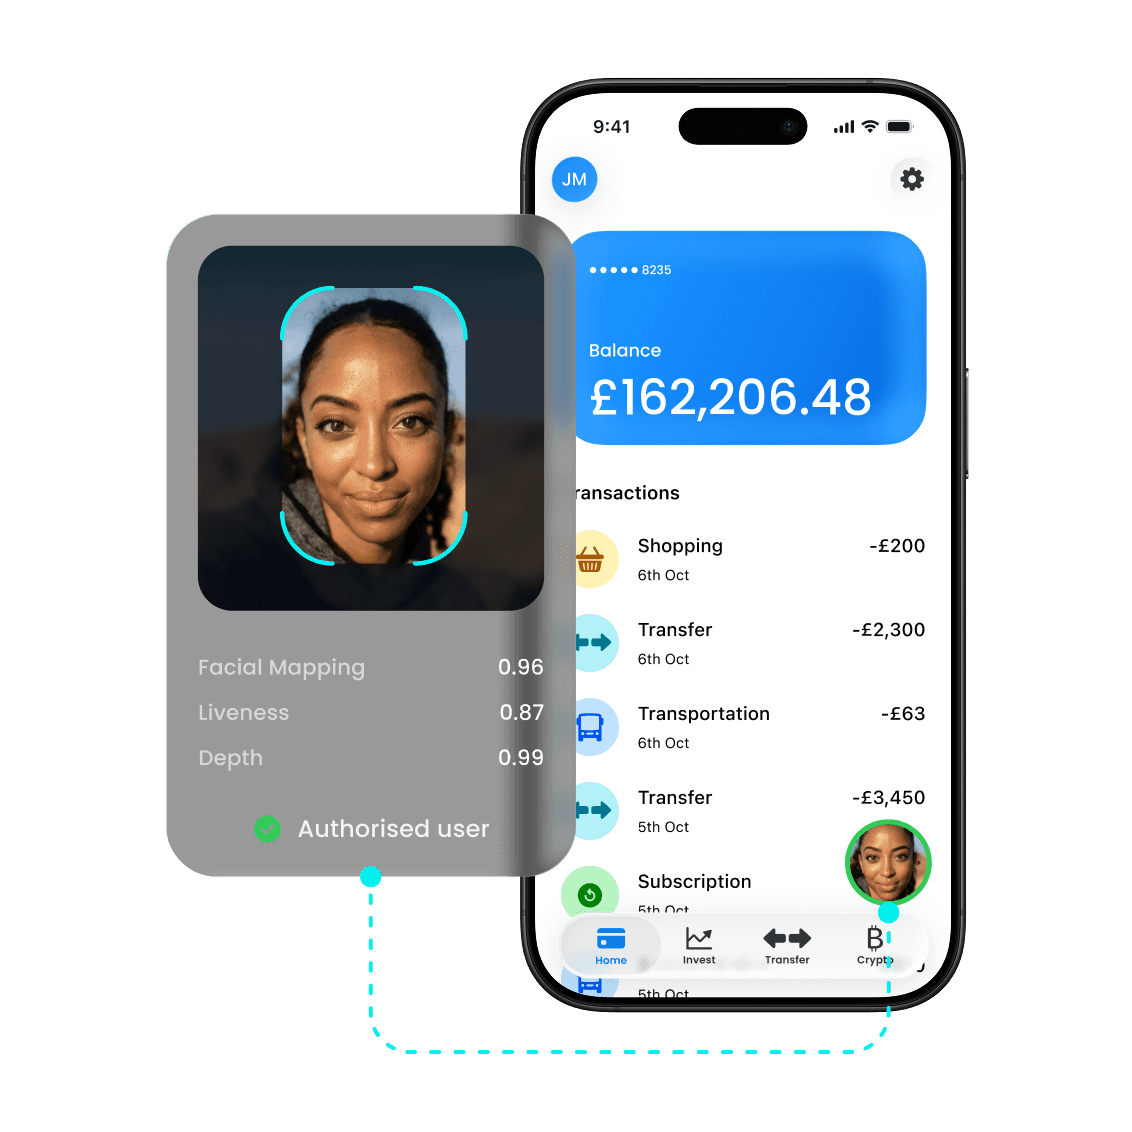
YEO CFR SDK
The YEO CFR SDK adds continuous session-layer verification to banking and payments platforms — verifying account holder presence at the point of transaction, not just at login, with no displacement of existing authentication infrastructure.

"/><stop offset="1" stop-color="rgb(207, 255, 245)"/></linearGradient></defs><g fill="transparent" height="45px" id="WgbicUNiZ" transform="translate(19 16)" width="45px"><path d="M 21.26 0 C 23.849 0 26.329 0.46 28.623 1.301 C 28.089 2.008 27.811 2.941 27.811 4.128 C 27.811 5.431 28.146 6.428 28.787 7.156 C 29.426 7.881 30.336 8.3 31.413 8.516 C 32.459 8.725 33.294 9.553 33.502 10.59 C 33.724 11.7 34.162 12.638 34.914 13.296 C 35.669 13.957 36.705 14.305 38.057 14.305 C 39.334 14.304 40.324 13.993 41.06 13.412 C 42.003 15.799 42.52 18.397 42.52 21.116 C 42.52 32.778 33.002 42.232 21.26 42.232 L 3.427 42.232 C 2.42 42.232 2.024 40.934 2.862 40.379 L 7.563 37.266 C 2.938 33.393 0 27.595 0 21.116 C 0 9.454 9.518 0 21.26 0 Z M 21.26 7.966 C 13.948 7.966 8.02 13.853 8.02 21.116 C 8.02 28.379 13.948 34.266 21.26 34.266 C 28.572 34.266 34.5 28.379 34.5 21.116 C 34.5 20.305 34.426 19.511 34.284 18.741 C 32.925 20.202 30.986 21.116 28.835 21.116 C 24.722 21.116 21.387 17.776 21.387 13.656 C 21.387 11.502 22.299 9.561 23.756 8.199 C 22.948 8.046 22.113 7.966 21.26 7.966 Z" fill="rgb(255, 255, 255)" height="42.2322793006897px" id="AB2KVZf6K" transform="translate(0 2.768)" width="42.52027308592545px"/><g fill="transparent" height="13.791765897448883px" id="CjePk4zf6" transform="translate(31.114 0)" width="13.885821925020025px"><g fill="transparent" height="13.791765897448883px" id="v3H_EKvq7" width="13.885821925020025px"><path d="M 13.886 6.896 C 13.886 7.613 13.301 8.194 12.579 8.194 L 8.386 8.194 L 8.386 12.358 C 8.386 13.15 7.74 13.792 6.943 13.792 C 6.146 13.792 5.5 13.15 5.5 12.358 L 5.5 8.194 L 1.307 8.194 C 0.585 8.194 0 7.613 0 6.896 C 0 6.179 0.585 5.598 1.307 5.598 L 5.5 5.598 L 5.5 1.433 C 5.5 0.642 6.146 0 6.943 0 C 7.74 0 8.386 0.642 8.386 1.433 L 8.386 5.598 L 12.579 5.598 C 13.301 5.598 13.886 6.179 13.886 6.896 Z" fill="rgb(255, 255, 255)" height="13.791765897448883px" id="Gx3Hq_JED" width="13.885821925020025px"/><path d="M 13.886 6.896 C 13.886 7.613 13.301 8.194 12.579 8.194 L 8.386 8.194 L 8.386 12.358 C 8.386 13.15 7.74 13.792 6.943 13.792 C 6.146 13.792 5.5 13.15 5.5 12.358 L 5.5 8.194 L 1.307 8.194 C 0.585 8.194 0 7.613 0 6.896 C 0 6.179 0.585 5.598 1.307 5.598 L 5.5 5.598 L 5.5 1.433 C 5.5 0.642 6.146 0 6.943 0 C 7.74 0 8.386 0.642 8.386 1.433 L 8.386 5.598 L 12.579 5.598 C 13.301 5.598 13.886 6.179 13.886 6.896 Z" fill="url(%23O3wQKObfr-3259696891-linear-gradient)" height="13.791765897448883px" id="O3wQKObfr" width="13.885821925020025px"/></g></g></g></svg>)
YEO for Business
YEO for Business provides regulated financial firms with a verified internal communications channel — evidencing not just what was communicated, but who communicated it, to the standard SMCR, MiFID II, and FCA Consumer Duty require.
Compliance and regulatory fit
YEO for Business supports regulatory obligations under SMCR, MiFID II, Market Abuse Regulation, and FCA Consumer Duty — providing a verified audit trail that evidences not just what was communicated, but who communicated it, confirmed at the time.