The attacker is already inside the session. Perimeter security won't find them.
Modern cyber attacks don't force the door. They walk through it — impersonating trusted identities, operating inside authenticated sessions, and exploiting the trust that follows a legitimate login.


The problem
The threat model has changed. Attackers are not primarily trying to defeat authentication. They are operating after it — inside sessions that opened legitimately, under identities that passed every check. 17.3 billion stolen session cookies are in active circulation. AI enables real-time executive impersonation at scale. During incident response — when decisions need to move fast and teams are under pressure — attackers impersonate leadership, compromise communications channels, and insert themselves into the approval chain. Every message authorising a payment, directing staff, or approving system access becomes a potential attack vector precisely when the organisation is least equipped to verify it.
Post-Authentication Attacks
Attackers are not trying to defeat authentication.
They operate after it — inside sessions that opened legitimately, under credentials that passed every check.
17.3 Billion Stolen Sessions
Stolen session cookies in active circulation allow attackers to resume authenticated sessions without triggering a new login event. The attack is already inside.
Incident Response Vulnerability
Under attack, communications channels are exploited, and leadership is impersonated. Every instruction authorising a payment or directing staff becomes a potential attack vector precisely when verification matters most.
How YEO serves cyber security
Close the Session Gap
Continuous session-layer verification confirms the right person remains present throughout — not just at login.
On-device processing means no central biometric store to compromise.
Verified Incident Response
YEO for Business provides communications infrastructure where every instruction during an incident comes from a confirmed, verified identity.
Continuous biometric verification, end-to-end encryption, and verified audit trail — even when every other system is under attack.
Protect the Approval Chain
Prevent attackers from inserting themselves into payment authorisation, staff direction, or system access approvals.
The communications channel itself cannot be impersonated, even under active compromise.
Relevant Solutions
Cerified identity at both layers: session and communications
Together, YEO's products close the session gap at both ends: verifying who is present in a user session, and ensuring every internal communication during an incident comes from a confirmed, verified identity.
YEO CFR SDK
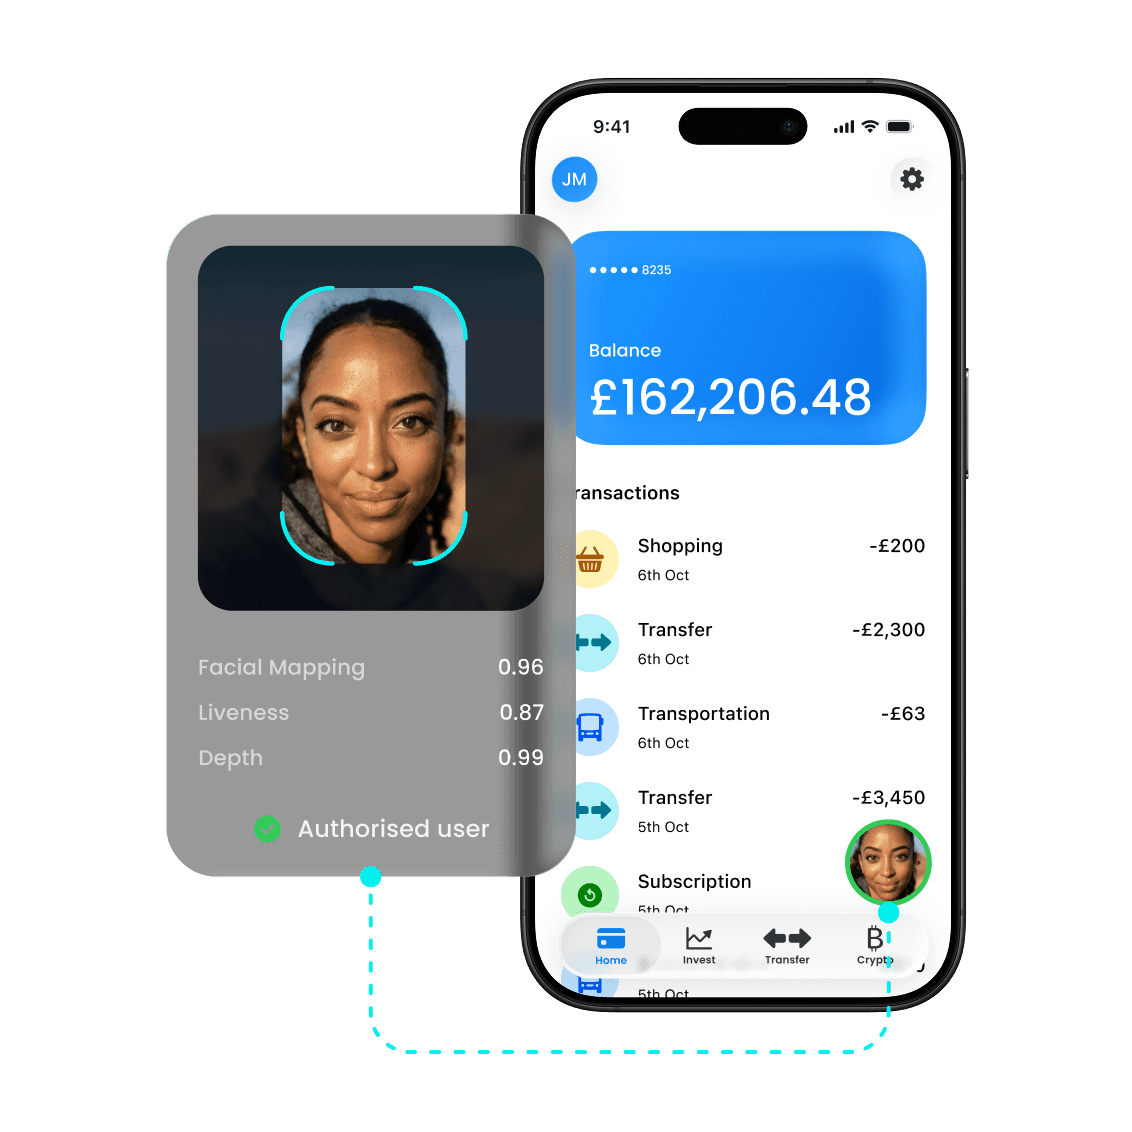
The YEO CFR SDK closes the session gap at the platform layer — verifying that the right person remains present throughout a session, not just at the point of login, with on-device processing and no central biometric store.

"/><stop offset="1" stop-color="rgb(207, 255, 245)"/></linearGradient></defs><g fill="transparent" height="45px" id="WgbicUNiZ" transform="translate(19 16)" width="45px"><path d="M 21.26 0 C 23.849 0 26.329 0.46 28.623 1.301 C 28.089 2.008 27.811 2.941 27.811 4.128 C 27.811 5.431 28.146 6.428 28.787 7.156 C 29.426 7.881 30.336 8.3 31.413 8.516 C 32.459 8.725 33.294 9.553 33.502 10.59 C 33.724 11.7 34.162 12.638 34.914 13.296 C 35.669 13.957 36.705 14.305 38.057 14.305 C 39.334 14.304 40.324 13.993 41.06 13.412 C 42.003 15.799 42.52 18.397 42.52 21.116 C 42.52 32.778 33.002 42.232 21.26 42.232 L 3.427 42.232 C 2.42 42.232 2.024 40.934 2.862 40.379 L 7.563 37.266 C 2.938 33.393 0 27.595 0 21.116 C 0 9.454 9.518 0 21.26 0 Z M 21.26 7.966 C 13.948 7.966 8.02 13.853 8.02 21.116 C 8.02 28.379 13.948 34.266 21.26 34.266 C 28.572 34.266 34.5 28.379 34.5 21.116 C 34.5 20.305 34.426 19.511 34.284 18.741 C 32.925 20.202 30.986 21.116 28.835 21.116 C 24.722 21.116 21.387 17.776 21.387 13.656 C 21.387 11.502 22.299 9.561 23.756 8.199 C 22.948 8.046 22.113 7.966 21.26 7.966 Z" fill="rgb(255, 255, 255)" height="42.2322793006897px" id="AB2KVZf6K" transform="translate(0 2.768)" width="42.52027308592545px"/><g fill="transparent" height="13.791765897448883px" id="CjePk4zf6" transform="translate(31.114 0)" width="13.885821925020025px"><g fill="transparent" height="13.791765897448883px" id="v3H_EKvq7" width="13.885821925020025px"><path d="M 13.886 6.896 C 13.886 7.613 13.301 8.194 12.579 8.194 L 8.386 8.194 L 8.386 12.358 C 8.386 13.15 7.74 13.792 6.943 13.792 C 6.146 13.792 5.5 13.15 5.5 12.358 L 5.5 8.194 L 1.307 8.194 C 0.585 8.194 0 7.613 0 6.896 C 0 6.179 0.585 5.598 1.307 5.598 L 5.5 5.598 L 5.5 1.433 C 5.5 0.642 6.146 0 6.943 0 C 7.74 0 8.386 0.642 8.386 1.433 L 8.386 5.598 L 12.579 5.598 C 13.301 5.598 13.886 6.179 13.886 6.896 Z" fill="rgb(255, 255, 255)" height="13.791765897448883px" id="Gx3Hq_JED" width="13.885821925020025px"/><path d="M 13.886 6.896 C 13.886 7.613 13.301 8.194 12.579 8.194 L 8.386 8.194 L 8.386 12.358 C 8.386 13.15 7.74 13.792 6.943 13.792 C 6.146 13.792 5.5 13.15 5.5 12.358 L 5.5 8.194 L 1.307 8.194 C 0.585 8.194 0 7.613 0 6.896 C 0 6.179 0.585 5.598 1.307 5.598 L 5.5 5.598 L 5.5 1.433 C 5.5 0.642 6.146 0 6.943 0 C 7.74 0 8.386 0.642 8.386 1.433 L 8.386 5.598 L 12.579 5.598 C 13.301 5.598 13.886 6.179 13.886 6.896 Z" fill="url(%23O3wQKObfr-3259696891-linear-gradient)" height="13.791765897448883px" id="O3wQKObfr" width="13.885821925020025px"/></g></g></g></svg>)
YEO for Business
YEO for Business provides security teams and leadership with a verified communications channel during an active incident — ensuring every instruction comes from a confirmed identity, even when every other system is compromised.